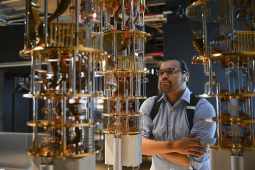
There’s bipartisan support for further investment in the U.S. quantum industry, along with worries that America’s industrial capacity won’t keep up with demand.
October’s wave of vulnerabilities and attacks earned a stark nickname: “Black October.” But was it an unprecedented crisis—or a glimpse of what’s becoming normal? On this episode…
Videostrong sold TV set-top boxes and other devices with pre-installed malware. The yearslong operation evaded Google’s security tests and established a botnet for cybercriminals.
Vapor Panda targeted more than 200 organizations spanning at least 14 countries, according to CrowdStrike. The ongoing campaign is remarkably successful and operating at shocking speed.
The China-linked threat group has used the “Silent Train” framework, built on a series of rapidly rotating compromised devices, to infiltrate hundreds of critical infrastructure networks.
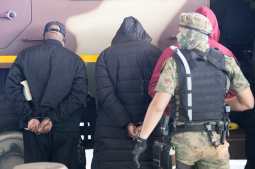
The U.S. District of Columbia’s Scam Center Task Force, the FBI’s field office in Honolulu and the U.S. Attorney’s Office for the District of Alaska made a trip to Madagascar in August to review electronic devices seized from scam compounds. (Getty Images)
Traffic streaks past the Department of Justice (DOJ) headquarters building late in the evening on May 18, 2024 in Washington, DC. (Photo by J. David Ake/Getty Images)
Zheng Zhao and his co-conspirators allegedly deceived 174 U.S. residents into sending funds to a globally coordinated fake investment operation with ties to Cambodia.
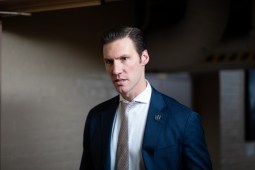
UNITED STATES – DECEMBER 10: Rep. Pat Harrigan, R-N.C., arrives for the House Republican Conference meeting in the U.S. Capitol on Wednesday, December 10, 2025. (Bill Clark/CQ-Roll Call, Inc via Getty Images)
One of the bill’s sponsors told CyberScoop it’s “incredibly expensive” for U.S. AI companies to stay ahead and distillation attacks incentivize stealing over innovation.
Storm-0940 used the agentic AI penetration testing framework to automate attacks and “reach more than 2,250 tenants at 2,900 sign-in attempts per minute,” Microsoft researchers said.