CyberScoop spoke with members of Congress, former federal law enforcement officials, cybersecurity attorneys and other experts about which laws, regulations or policies might apply to agentic hacks carried out by models at Anthropic, OpenAI, Meta, Google and other companies. (Image via Getty)
Experts and policymakers want AI companies to face consequences for agentic hacks. There may not be a clear-cut answer under existing laws and regulations.
SAN FRANCISCO, CALIFORNIA – SEPTEMBER – 15: Nvidia CEO Jensen Huang speaks during the keynote address at Salesforce’s Dreamforce conference at the Moscone Center on September 15, 2026 in San Francisco, California. Dreamforce is an annual event that highlights the company’s technologies and encourages professional networking. (Photo by Benjamin Fanjoy/Getty Images)
One expert told CyberScoop that the announcement reflects industry recognition that after years of training models to behave safely or ethically, more outside controls are needed.
Boston, MA – August 29: Senator Ed Markey addresses his supporters during a ‘Power to the People’ rally at the IBEW Local 103 facility on August 29, 2026. (Photo by Craig F. Walker/The Boston Globe via Getty Images)
A new Democratic bill in Congress would establish a federal Cybersecurity and AI Board of Investigations to provide independent government oversight of cyberattacks carried out by AI…
The white paper is the latest step in trying to create a “Quality Era” for the Common Vulnerabilities and Exposures (CVE) program as the number of CVEs…
Dmytro Kushneruk, Consul General of Ukraine in San Francisco, speaks at at Sept. 23, 2026 event in New York City about a partnership with OpenAI to use their cyber models to protect critical infrastructure from cyber attacks. (Image: OpenAI)
A Ukrainian official said the government will use the tools to automate cybersecurity functions in critical infrastructure as the war with Russia continues.
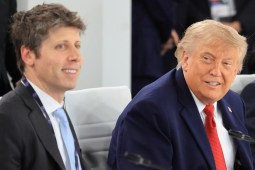
US President Donald Trump (C) and Open AI CEO Sam Altman (L) react during a working lunch meeting of G7 members, partner countries, and artificial intelligence business leaders as part of the G7 summit, in Evian, eastern France, on June 17, 2026. A G7 summit is set to take place June 15 to 17 in the French town of Evian-les-Bains near Switzerland and it will be attended by country leaders as well as the EU’s foreign policy chief and ministers from Brazil, Canada, the United Arab Emirates and Turkey. (Photo by Ludovic MARIN / AFP via Getty Images)
Following a series of chaotic agentic hacks, Trump and administration officials have consistently expressed fears of Chinese AI dominance in pushing for fewer regulations.
Researchers at Hacktron discovered a vulnerability, HEIF Heist, named for its ability to trigger memory corruption errors in affected software, allowing the attacker to pilfer sensitive data from its victims. (Image Source: Getty)
The bug, since patched, gave attackers remote code execution privileges and access to user accounts and production environments, including Meta’s core product suite and an OpenAI software…
In recent conversations, cybersecurity and national security professionals raised questions about both the technical solutions OpenAI and Anthropic use to contain their models, as well as the glaring absence of federal oversight from federal regulators or truly independent third-party review. (Image via Getty)
While large language models present real risks to society, experts say they can be tested and largely controlled using well-worn cybersecurity and policy choices.
Richard Grabowski, acting branch chief of service delivery and deputy program manager for CISA’s CDM program, speaks at the Elastic Federal Cyber Defense Breakfast produced by FedScoop on Sept. 15, 2026. (Scoop News Group)
OpenAI confirmed it was investigating an incident in May where the company’s AI agents uploaded thousands of malicious software packages to a public code repository RubyGems. (Source: RubyGems)
OpenAI confirmed their agents were behind a campaign in May that researchers say flooded the popular online code repository with malicious software packages.