How CISA is prioritizing companies for talks about security improvements
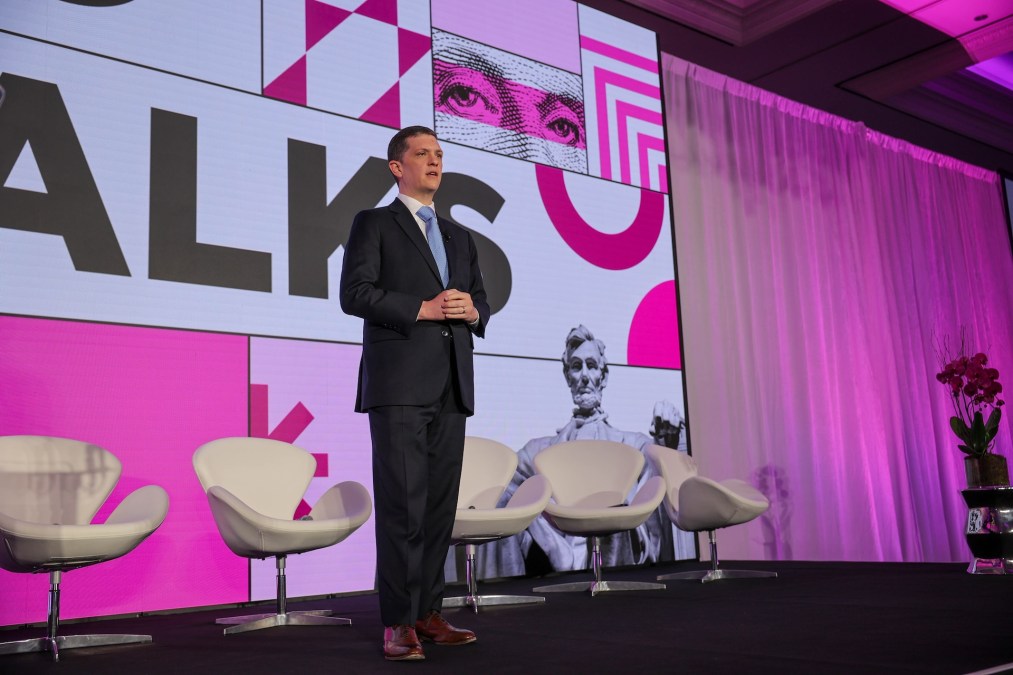
The Cybersecurity and Infrastructure Security Agency has identified approximately 100 companies that own critical infrastructure for talks on hardening their systems because of how vital they are to the nation, CISA acting director Nick Andersen said Tuesday.
That figure does not cover everyone CISA wants to speak with, because those companies have so many interdependencies with other firms, he said. And the conversations are going to vary wildly from company to company, he told CyberScoop.
“For the initial workstream, we’re probably talking about around 100 companies,” Andersen said after speaking at FedTalks, produced by FedScoop. “We want to be focused on being able to gather what are those lessons learned that are most appropriate coming out of it, what works and what doesn’t, and the problem with each one of those different companies.”
To generate the list, CISA went through an intergovernmental Homeland Defense Working Group that identified companies that provide functions deemed most important to the economy, public health and safety, national security and defense critical infrastructure.
Then, Andersen said, the agency overlaid five to six years of intelligence about what cyber adversaries appeared to value most, such as where they were pre-positioning or where their research and development budgets were going. Companies that appeared on both lists became the targets for “initial engagement,” which also meant involving the right sector risk management agencies.
So hypothetically, if the decision is that a particular port is especially important, CISA would talk to the port operator. “But I also need to have a conversation with their energy provider, with their telecommunications provider, et cetera, et cetera, et cetera,” he said.
In his FedTalks speech Andersen said the ideal is to have conversations that include IT and operational technology providers, along with cybersecurity providers. He said the goal is to advance the agency’s “CISA 2030” strategy, which focuses on resilience, minimum viability and related priorities.
“It’s going to continue to result in several significant, important conversations over the coming weeks and months about, what does it mean to appropriately invest?” Andersen said. “What does it mean to collaborate with one another on that longer-term resilience as we move forward? That’s going to have to be a collective effort across our communities.“
So far, he said, the conversations have been productive.
“A lot of this has also included things like CI-Fortify assessments with those companies, which have been really really good conversations for us to be able to have around, what does it mean to be able to plan for isolation and recovery?” Andersen said.
Andersen, and other Trump administration officials, have spoken in recent months about the need to be selective in how they prioritize vulnerabilities and hacking targets.