Russian Turla group used new toolset to silently pilfer emails from Kazakhstan, Romanian governments
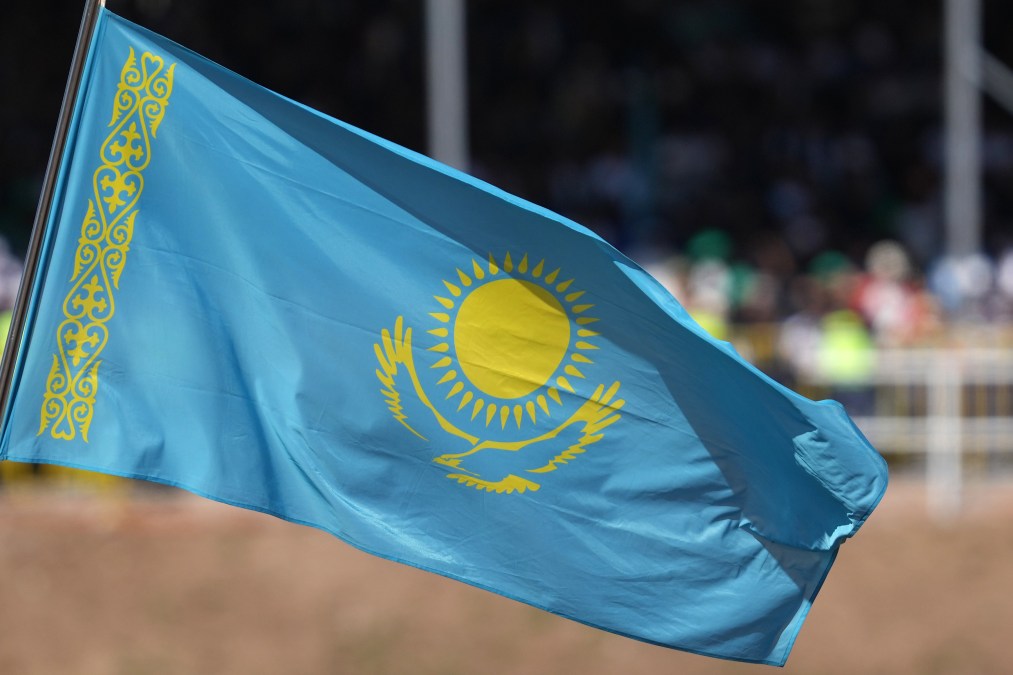
Turla, a notorious cyberespionage group aligned with the Russian government, has been wielding a new, customizable toolset to compromise governments around the world over the past year, including Kazakhstan.
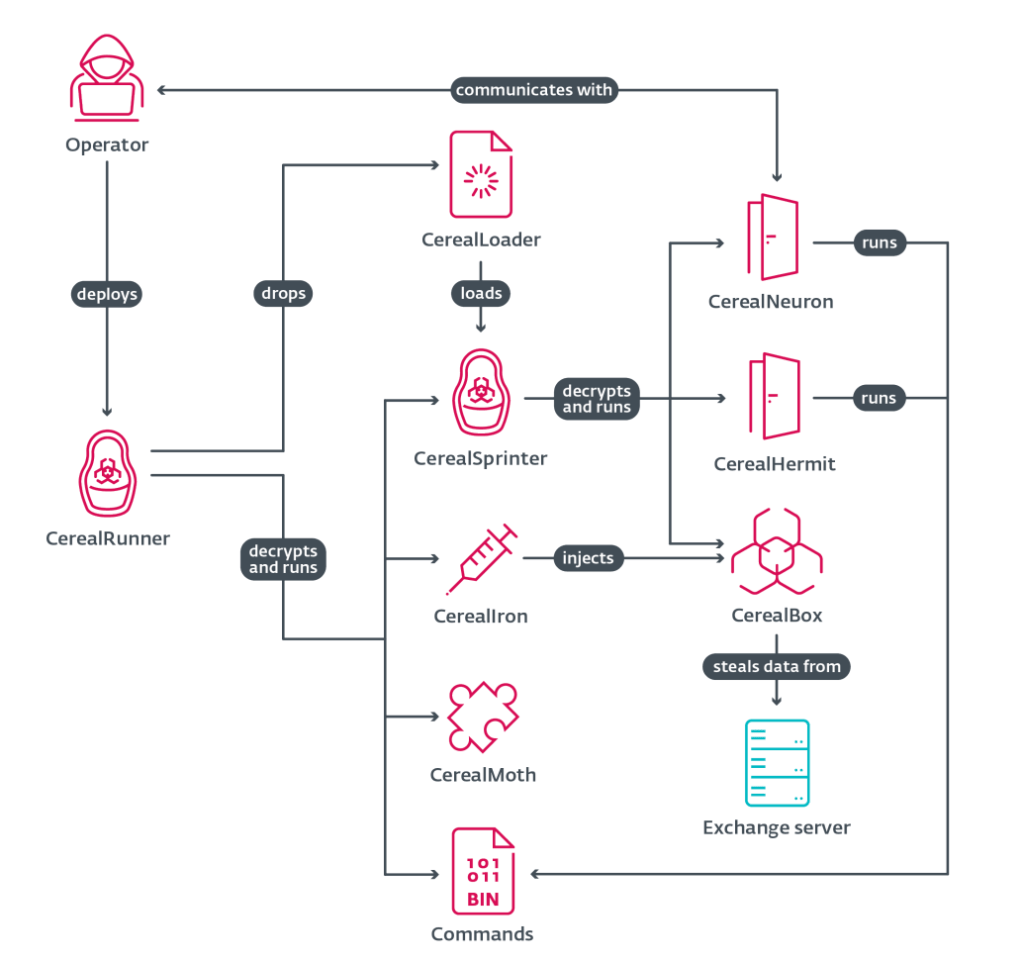
The toolset was first discovered in November 2025 by cybersecurity firm ESET, which named it “Turla’s Cereal” as a play on its highly modular, interconnected and “serialized” design. It chains and exploits different legitimate functions across Microsoft Exchange, Windows, and .NET assemblies, which Microsoft has described as “the fundamental units of deployment, version control, reuse, activation scoping, and security permissions for .NET-based applications.”
“One of the most interesting aspects of this toolset is what we did not find: external command and control infrastructure,” ESET researcher Matías Porolli wrote in the report, released Tuesday. “Instead — adding insult to injury — the victim’s compromised Exchange server is co-opted to act as the C&C infrastructure.”
Multiple Western governments and threat intelligence firms have attributed Turla as a part of Russia’s Federal Security Service (FSB), which is tasked with gathering intelligence on foreign governments, businesses and organizations. According to MITRE, the group has compromised victims in more than 50 countries, spanning governments, militaries, private-sector companies and research organizations.
Porolli said the toolset was found on a compromised Exchange server used by the government of Kazakhstan on Nov. 28, 2025, where it could receive commands, execute in memory, gather intel on the organization and collect certain email messages.
Another version found inside a Romanian government agency a month later was configured to target emails sent to or received by the Western powers — the European Union and the North Atlantic Treaty Organization — adversarial with Russia. At the time, Romanian politicians were calling for a NATO mission in the Black Sea to deter what they viewed as Russian aggression. In July, the EU announced sanctions against Russian individuals and organizations, citing a yearslong cyberespionage campaign from Turla and other Russian groups against European nations as well as the targeting of Poland’s energy grid and European businesses by Russia-aligned hacking groups.
According to ESET, the toolset lacks many features used to identify malware, such as implants, beaconing back to command-and-control infrastructure or built-in command lists. Most executables are performed in-memory using temporary storage to avoid leaving evidence, while commands written to permanent memory are delivered via encrypted payloads.
One component, dubbed CerealNeuron, operates as the main backdoor but does not beacon back to its operator the way many pieces of malware do. Instead, it runs on the compromised server and “passively listens for incoming web requests on paths that look like ordinary Exchange traffic.” The result is an attack that leaves no domain, IP address, hosting provider or timing patterns for defenders to find and block.
“The Cereal toolset demonstrates that, for Turla, Exchange servers are not just mail servers — they are durable collection points, internal execution hubs, and a suitable environment for hiding sophisticated .NET tradecraft,” Porolli wrote.