Government auditors say federal agencies haven’t met mandated security steps for operational technology, which hackers targeted in water sector attacks this summer.
The vendor was much quicker and consistent in its response to the latest defect, and researchers consider the impact relatively low compared to the previous pair of…
Internet-exposed tech, PLCs, outside integrators and inside protections are all factors the water sector’s information sharing and analysis center is watching.
Biotechnology doesn’t have its own critical infrastructure designation, so the bipartisan group of lawmakers wants to make sure it’s protected like it.
The white paper is the latest step in trying to create a “Quality Era” for the Common Vulnerabilities and Exposures (CVE) program as the number of CVEs…
In this photo illustration, the United States Cybersecurity and Infrastructure Security Agency (CISA) logo is seen displayed on a smartphone screen. (Photo Illustration by Thomas Fuller/SOPA Images/LightRocket via Getty Images)
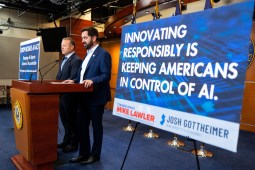
Rep. Josh Gottheimer, D-N.J., left, and Rep. Mike Lawler, R-N.Y., hold a news conference on the Stop Rogue AI Act in the U.S. Capitol on Thursday, September 17, 2026. (Bill Clark/CQ-Roll Call, Inc via Getty Images)
A key House Democrat and his bipartisan sponsors want to see a $100 million DHS pilot to help critical infrastructure owners and operators — separate from another…