In recent conversations, cybersecurity and national security professionals raised questions about both the technical solutions OpenAI and Anthropic use to contain their models, as well as the glaring absence of federal oversight from federal regulators or truly independent third-party review. (Image via Getty)
While large language models present real risks to society, experts say they can be tested and largely controlled using well-worn cybersecurity and policy choices.
OpenAI confirmed it was investigating an incident in May where the company’s AI agents uploaded thousands of malicious software packages to a public code repository RubyGems. (Source: RubyGems)
OpenAI confirmed their agents were behind a campaign in May that researchers say flooded the popular online code repository with malicious software packages.
The Republican lawmaker called OpenAI’s leadership decisions “reckless,” and used recent warnings about the existential risk of AI to bolster his inquiry.
The company says the breach stemmed from a systemic failure of alignment and security, and has taken measures to prevent agents from independently orchestrating complex cyberattacks.
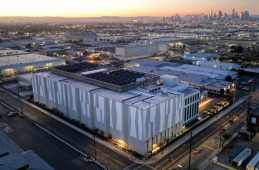
A data center in Vernon, Calif. They are groups calling for AI, and the technology it sits on, to be designated as critical infrastructure. (Getty Images)
The designation would unlock a range of federal services, tools and resources for an industry that policymakers view as increasingly tied to national and economic security.
In this photo illustration, the Anthropic logo is seen on a smartphone. (Photo Illustration by Algi Febri Sugita/SOPA Images/LightRocket via Getty Images)
As frontier models and their sandbox escaping exploits dominate front-page news, researchers are increasingly worried about cheaper, more efficient AI models.
In a pair of blogs posted Monday, OpenAI said it was updating its Daybreak program – which provides unreleased frontier models to private organizations and governments for defensive cybersecurity work – and introducing a new model variant. (Photo by Samuel Boivin/NurPhoto via Getty Images)
Research finds your AI generated security patch is more likely to fail than fully fix a vulnerability. It might even introduce brand new flaws to exploit along…
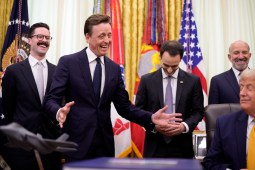
United States National Cyber Director Sean Cairncross (2nd-L) accompanied by United States Chief Technology Officer Dr. Ethan Klein (L), White House Office of Science and Technology Policy Director Michael Kratsios (3rd-L), U.S. President Donald Trump (R), and Commerce Secretary Howard Lutnick (2nd-R), speaks during an event in the Oval Office of the White House on June 22, 2026 in Washington, D.C. (Photo by Andrew Harnik/Getty Images)
The Trump administration executive order on artificial intelligence tried to strike the balance between responsible use, security and mutual benefit, all with an eye toward not making…