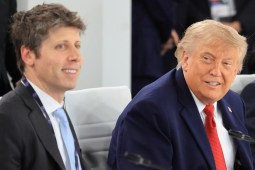
US President Donald Trump (C) and Open AI CEO Sam Altman (L) react during a working lunch meeting of G7 members, partner countries, and artificial intelligence business leaders as part of the G7 summit, in Evian, eastern France, on June 17, 2026. A G7 summit is set to take place June 15 to 17 in the French town of Evian-les-Bains near Switzerland and it will be attended by country leaders as well as the EU’s foreign policy chief and ministers from Brazil, Canada, the United Arab Emirates and Turkey. (Photo by Ludovic MARIN / AFP via Getty Images)
Following a series of chaotic agentic hacks, Trump and administration officials have consistently expressed fears of Chinese AI dominance in pushing for fewer regulations.
A Department of Transportation rule published last week says that airlines complying with cybersecurity regulations will have reduced customer obligations in the event of an attack.
The policy, passed under the Biden administration, forced health apps to disclose when users’ personal health records were exposed in a breach or shared without authorization.
The seal for the Federal Communications Commission (FCC) is seen in the agency’s briefing room during a meeting at headquarters on Feb. 18, 2026 in Washington, D.C. (Photo by Kevin Dietsch/Getty Images)
The rules have already been rejected by multiple state courts, but the Trump administration said it’s preparing in case of a favorable Supreme Court decision.
This week, FTC Chair Andrew Ferguson sent letters to private-sector companies detailing how the commission intends to police compliance once enforcement begins. (Getty Images)
The commission is mulling whether to begin regulating bias in AI systems. Critics say they’re overstepping their legal authority and infringing on free speech.
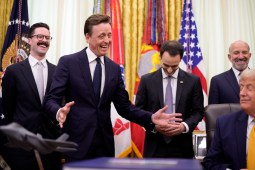
United States National Cyber Director Sean Cairncross (2nd-L) accompanied by United States Chief Technology Officer Dr. Ethan Klein (L), White House Office of Science and Technology Policy Director Michael Kratsios (3rd-L), U.S. President Donald Trump (R), and Commerce Secretary Howard Lutnick (2nd-R), speaks during an event in the Oval Office of the White House on June 22, 2026 in Washington, D.C. (Photo by Andrew Harnik/Getty Images)
The Trump administration executive order on artificial intelligence tried to strike the balance between responsible use, security and mutual benefit, all with an eye toward not making…
Digital legal compliance and government regulation concept with security icons, creative graphic style, on blurred US flag background. 3D Rendering. ismagilov, istock/Getty Images Plus
The GAO found 80 out of 117 rules that “either contain the same kind of reporting requirement applicable to a sector or the same reporting requirement as at least one other regulation.” (Getty Images)