SpyCloud’s study found 1,787 of the approximately 10,000 U.S. organizations had it, including one infected device that saved logins for 167 utility metering tenants.
Researchers at Hacktron discovered a vulnerability, HEIF Heist, named for its ability to trigger memory corruption errors in affected software, allowing the attacker to pilfer sensitive data from its victims. (Image Source: Getty)
The bug, since patched, gave attackers remote code execution privileges and access to user accounts and production environments, including Meta’s core product suite and an OpenAI software…
The latest zero-day has a maximum-severity rating and affects Cisco Identity Services Engine, a product hit with three actively exploited vulnerabilities since June 2025.
In recent conversations, cybersecurity and national security professionals raised questions about both the technical solutions OpenAI and Anthropic use to contain their models, as well as the glaring absence of federal oversight from federal regulators or truly independent third-party review. (Image via Getty)
While large language models present real risks to society, experts say they can be tested and largely controlled using well-worn cybersecurity and policy choices.
It’s the first guidance from the Cybersecurity and Infrastructure Security Agency on deploying decoys, like honeypots, to detect and distract adversaries.
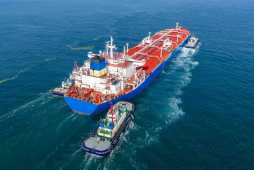
The agencies issued a joint statement saying the “joint security boardings” came in response to “indications that the networks of both vessels were compromised.”
One flaw allows an unauthenticated attacker to read files from the server. GitLab urged operators of self-managed installations to upgrade immediately.
The Department of Justice building is seen in Washington, DC, on August 9, 2022. (Photo by Stefani Reynolds / AFP) (Photo by STEFANI REYNOLDS/AFP via Getty Images)