The China-linked threat group has used the “Silent Train” framework, built on a series of rapidly rotating compromised devices, to infiltrate hundreds of critical infrastructure networks.
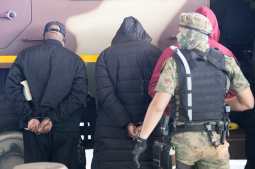
The U.S. District of Columbia’s Scam Center Task Force, the FBI’s field office in Honolulu and the U.S. Attorney’s Office for the District of Alaska made a trip to Madagascar in August to review electronic devices seized from scam compounds. (Getty Images)
Storm-0940 used the agentic AI penetration testing framework to automate attacks and “reach more than 2,250 tenants at 2,900 sign-in attempts per minute,” Microsoft researchers said.
Researchers said the first known attack by Armory Castle, also known as UNC5221, occurred almost seven weeks ago. The threat group previously compromised Ivanti and Citrix customers.